Impact assessments · DPDP s.10, Rule 13

Assessments that are linked, not filed.

A Significant Data Fiduciary must assess; everyone else should before a risky new purpose. In Nyvika an assessment is attached to the real purposes, stores and processors it covers, so it is never a document nobody can find.

s.10(2)(c) DPIARule 13 SDF dutiesReview workflow
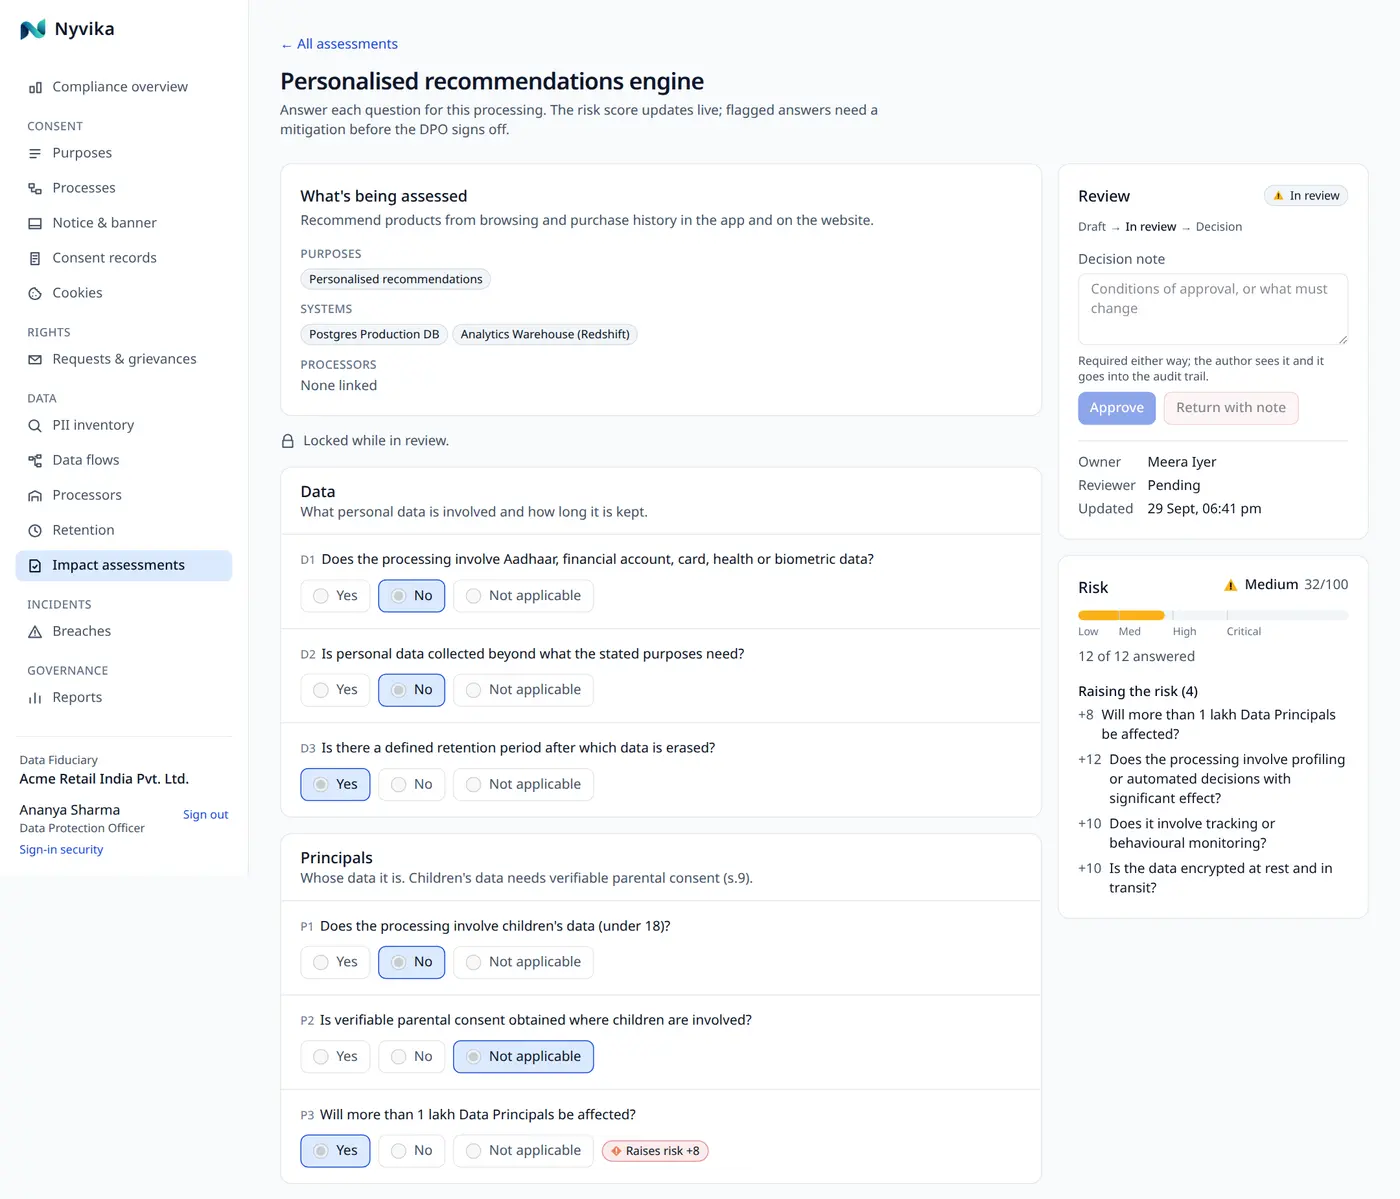
An impact assessment in the console: scope, questionnaire scores, mitigations and review status
The challenge

An assessment nobody reads again.

A DPIA written as a document in a shared folder is complete on the day it is signed and wrong a month later. The Act expects it to describe the processing as it actually is.

s.10
Significant Data Fiduciaries must
Periodic DPIAs, audits and a resident Data Protection Officer. The assessment has to exist, be current and be reviewable.
Scope
Which systems does it cover?
If the assessment does not name the stores and processors, nobody can tell whether a new system changed the answer.
Follow-through
Mitigations without owners
Risks identified and never assigned are a record of what you knew and did not do.
What Nyvika does

Scope, score, review.

Choose what the assessment covers, answer the questionnaire, assign the mitigations, submit for review.

Linked scope

An assessment names the purposes, data stores and processors it covers, drawn from the registers.

  • Changes to those registers are visible from the assessment
  • Data categories and identifier types pulled from discovery
  • One assessment per processing activity

Scored questionnaire

Necessity, proportionality, security, rights, transfers and children's data, scored to a risk level.

  • Transparent scoring, documented
  • Risk level shown on the register
  • Notes per answer

Mitigations and owners

Each risk gets a mitigation, an owner and a status.

  • Open mitigations on the overview
  • Closed with a note and date
  • Reviewer sees them before approving

Review workflow

Draft, submitted, approved or returned, with the reviewer recorded.

  • DPO approval for Significant Data Fiduciaries
  • Register report of every assessment
  • Audit log of each state change
One ledger

How it connects.

Every module writes to the same registers and the same hash-chained evidence, so nothing is re-keyed and nothing is lost between teams.

Questions

Asked about impact assessments.

Do we need a DPIA if we are not a Significant Data Fiduciary?

The Act only mandates it for SDFs. It is still the clearest way to show reasonable safeguards for a new or risky purpose, and the questionnaire takes an hour, not a week.

Does Nyvika suggest risks with AI?

No. The questionnaire is fixed and documented, and the scoring is transparent. Your team answers from knowledge of the processing, which is what a reviewer wants to see.

Can we attach our own template?

Not in this release. The questionnaire covers the elements a DPIA under the Rules is expected to, and notes on each answer hold the detail your template would.

Still have a question? Write to us.

Assess your riskiest purpose today.

In the demo we open an assessment on one of your purposes and score it with your team in the room.